
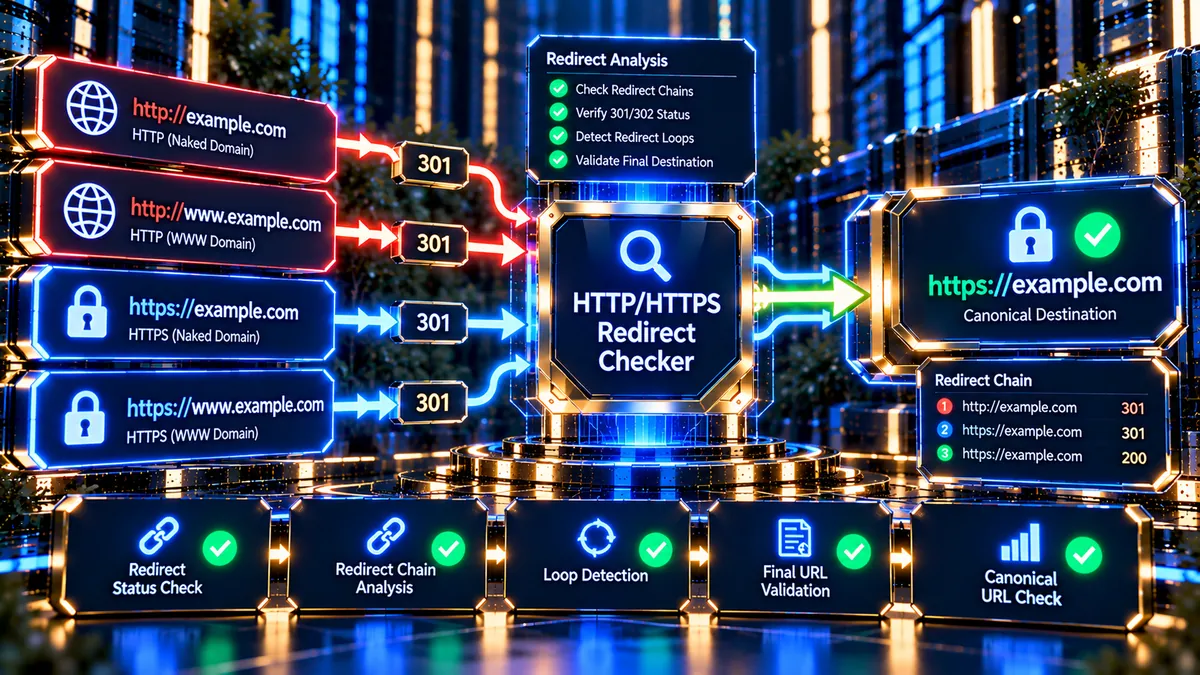
Free HTTP/HTTPS Redirect Checker
The PKCapra HTTP/HTTPS Redirect Checker is a free technical SEO diagnostic tool that analyzes how all major HTTP and HTTPS hostname variations resolve for a domain.
A website can be accessed through multiple protocol and hostname combinations, including the naked domain and the www version. If these variations do not consistently resolve to one preferred secure destination, the website can develop redirect chains, temporary redirects, inconsistent canonical signals, or insecure final destinations.
The PKCapra HTTP/HTTPS Redirect Checker automatically tests four core URL variations:
- HTTP Naked
- HTTP WWW
- HTTPS Naked
- HTTPS WWW
It follows the redirect path for each variation and reports the HTTP status, redirect count, final destination, security status, and whether the variations agree on a single canonical HTTPS destination.
The tool is designed for website owners, WordPress developers, technical SEO professionals, agencies, hosting administrators, and anyone troubleshooting domain redirect architecture.
It runs server-side and does not require a third-party redirect analysis API.
HTTP/HTTPS Redirect Checker
Compare all four core protocol and hostname variations, trace redirects, and identify the final HTTPS canonical destination.
HTTP/HTTPS redirect architecture
—
Protocol and hostname comparison
| Variation | Initial URL | Final Status | Redirects | Final Destination | Validation |
|---|
Designated HTTPS choice
Optimization status
Native cURL redirect trace
HTTP/HTTPS canonicalization checkpoints
The checker performs four independent server-side cURL requests with native redirect following. Final destinations are normalized for scheme, hostname, default ports, and trailing root slashes before canonical agreement is evaluated.
What Is an HTTP/HTTPS Redirect Checker?
An HTTP/HTTPS Redirect Checker is a technical diagnostic tool that examines how different protocol and hostname versions of a website resolve.
A typical domain can have four primary combinations:
http://example.comhttp://www.example.comhttps://example.comhttps://www.example.com
These variations can produce different redirect behaviors if the website has not been configured consistently.
For example, a website may intentionally establish:
as its preferred secure destination.
In that architecture, the other variations should ultimately resolve toward that destination through an appropriate redirect structure.
The PKCapra HTTP/HTTPS Redirect Checker tests these variations independently so that problems affecting only one version are easier to identify.
Why Redirect Consistency Matters
Redirects are an important part of technical website architecture.
They help establish relationships between alternative URLs and can guide users and crawlers toward the intended destination.
Inconsistent redirect behavior can create problems such as:
- Redirect chains
- Temporary redirects
- Multiple accessible URL versions
- HTTP final destinations
- HTTPS hostname inconsistencies
- Incorrect redirect targets
- Unnecessary redirect hops
- Conflicting canonical signals
For example, consider these four variations:
http://example.com
http://www.example.com
If all four eventually resolve to:
the website has a clearly defined secure destination.
If one variation instead ends at http://example.com/, another ends at https://example.com/, and another requires several intermediate redirects, the URL architecture requires further investigation.
For a broader technical review, use the Full SEO Site Audit to analyze redirect architecture together with other technical SEO signals.
The Four Redirect Variations Tested
The PKCapra HTTP/HTTPS Redirect Checker tests exactly four core variations.
1. HTTP Naked Domain
The first variation uses the non-secure protocol with the root hostname:
http://example.com
This tests how the basic HTTP version of the domain behaves.
A correctly configured website will normally redirect this request toward the intended HTTPS destination.
2. HTTP WWW Domain
The second variation uses HTTP with the www hostname:
http://www.example.com
This verifies whether the www version follows the same redirect architecture as the naked domain.
3. HTTPS Naked Domain
The third variation uses HTTPS with the root hostname:
This is one of the two secure versions and may either be the preferred canonical destination or redirect to the preferred www version.
4. HTTPS WWW Domain
The fourth variation uses HTTPS with the www hostname:
This may be the designated canonical destination when a website uses www as its preferred hostname.
The checker compares the final results of all four variations to determine whether the domain has a consistent secure destination.
How the Redirect Engine Works
Each of the four URL variations is tested independently.
The diagnostic engine records important response information including:
- Initial URL
- HTTP response status
- Redirect count
- Redirect destination
- Final destination URL
- Final HTTP status
- Secure or insecure final protocol
- Redirect chain information
- Destination agreement
The four requests are not treated as one combined request.
Each variation receives its own diagnostic so that differences between the domain versions remain visible.
Redirect Count Analysis
Redirect count identifies how many redirect hops are required before a request reaches its final destination.
For example:
http://example.com
→ 301
→ https://www.example.com
contains one redirect hop.
A more complicated path may look like:
http://example.com
→ 301
→ https://example.com
→ 301
→ https://www.example.com
This contains multiple redirect hops.
The second architecture may still reach the correct secure destination, but it introduces an unnecessary intermediate step if the intended architecture can redirect directly to the final canonical URL.
The checker therefore treats redirect chains as an optimization or configuration issue rather than automatically treating every multi-hop result as a fatal failure.
Understanding 301 Redirects
A 301 response indicates a permanent redirect.
For a website that permanently prefers HTTPS, a common architecture is:
http://example.com
→ 301
→ https://example.com
or:
http://example.com
→ 301
→ https://www.example.com
depending on the site’s preferred hostname.
A direct permanent redirect can provide a simple and efficient path to the intended destination.
Understanding 302 Redirects
A 302 response represents temporary redirect behavior.
For a website that is permanently enforcing HTTPS and a preferred hostname, a temporary redirect may require review.
A 302 is not automatically an error because there are legitimate situations where temporary redirects are intentional.
However, if the website’s permanent architecture is supposed to be HTTPS plus a specific hostname, the redirect configuration should be reviewed.
Understanding 307 Redirects
A 307 Temporary Redirect also represents temporary redirect behavior.
The browser or client is instructed to temporarily use another URL while preserving the request method semantics associated with the redirect.
For normal website protocol canonicalization, a 307 may therefore deserve review if permanent HTTPS enforcement is intended.
Understanding 308 Redirects
A 308 Permanent Redirect communicates permanent redirection while preserving request method semantics.
The PKCapra checker records the actual status returned by the server rather than treating every permanent redirect as a 301.
This distinction is useful when diagnosing modern web infrastructure, reverse proxies, CDNs, and application routing.
Canonical Destination Analysis
One of the most important features of the HTTP/HTTPS Redirect Checker is the Canonical Destination Test.
The checker examines where each of the four variations ultimately resolves.
The objective is to determine whether the variations converge on one secure destination.
For example:
- HTTP Naked →
https://www.example.com/ - HTTP WWW →
https://www.example.com/ - HTTPS Naked →
https://www.example.com/ - HTTPS WWW →
https://www.example.com/
This represents strong destination agreement.
The checker normalizes relevant URL components when comparing destinations so that harmless formatting differences do not automatically produce a false mismatch.
The analysis considers:
- Protocol
- Hostname
wwwvariation- Default ports
- Trailing root slash
- Path
- Query parameters
- Fragment handling
The objective is to identify the actual destination architecture rather than relying on brittle raw URL string equality.
What Is a Canonical Choice?
The Canonical Choice is the secure HTTPS destination that the checker identifies as the designated final destination for the domain’s four protocol and hostname variations.
A healthy redirect architecture generally has one clear preferred destination.
For example:
may be the canonical choice when the website intentionally uses www.
Alternatively:
may be the canonical choice for a naked-domain architecture.
The tool does not require every website to use www or every website to use the naked domain.
Instead, it evaluates whether the four tested variations consistently agree on the site’s chosen secure destination.
Green Redirect Status
A Green result indicates that the redirect architecture satisfies the tool’s optimal configuration criteria.
Typical Green conditions include:
- Final destination uses HTTPS
- All four variations agree on the same secure destination
- HTTP variations use a direct permanent redirect where appropriate
- Redirect chains are avoided
- Final response is successful
- No critical timeout occurs
- No final insecure HTTP destination occurs
A Green result indicates that the tested redirect architecture is consistent according to the diagnostic rules.
Yellow or Orange Redirect Status
Yellow or Orange indicates that the website reaches a usable destination but the redirect architecture may require review.
Examples include:
- 302 Temporary Redirect
- 307 Temporary Redirect
- Multiple redirect hops
- Variations resolving to different secure destinations
- Non-uniform hostname behavior
- Other non-optimal redirect patterns
A Yellow result does not automatically mean the website is broken.
It indicates that the redirect structure may be less efficient or less consistent than the preferred configuration.
Red Redirect Status
Red indicates a critical redirect or response problem.
Examples include:
- Request timeout
- cURL failure
- Server response failure
- 4xx final response
- 5xx final response
- Final destination remains HTTP
- Critical redirect failure
- Diagnostic crash or transport failure
A Red result should be investigated before considering the redirect architecture complete.
Redirect Chains
A redirect chain occurs when a URL passes through multiple redirect destinations before reaching its final page.
For example:
http://example.com
→ 301
→ http://www.example.com
→ 301
→ https://www.example.com
contains multiple redirect hops and includes an intermediate insecure HTTP destination.
A more efficient architecture can often send the initial request directly to the final secure destination.
For example:
http://example.com
→ 301
→ https://www.example.com
Reducing unnecessary redirect hops can simplify website architecture and reduce additional request processing.
Redirect Loops
A redirect loop occurs when URLs repeatedly redirect between destinations without reaching a final response.
For example:
http://example.com
→ https://example.com
→ http://example.com
can create an endless redirect cycle.
Redirect loops can prevent users and crawlers from reaching the intended content.
They can be caused by:
- Conflicting server rules
- CDN configuration
- Reverse proxy settings
- WordPress plugins
- HTTPS detection problems
- Incorrect proxy headers
- Application-level redirects
A redirect loop should be resolved at the configuration layer responsible for generating the conflicting responses.
HTTP Final Destination
A secure redirect architecture should ultimately reach an HTTPS destination when HTTPS is intended to be the canonical transport.
If one of the four tested variations ultimately finishes at an HTTP URL, the checker classifies that condition as critical.
For example:
→ 302
→ http://example.com
represents a regression from secure to insecure transport and should be investigated.
HTTPS Final Destination
A final HTTPS destination confirms that the tested variation ultimately reaches the secure protocol.
However, HTTPS alone does not prove that the destination is the correct canonical hostname.
The checker therefore evaluates both:
- Secure protocol
- Destination hostname agreement
This distinction helps separate a secure but inconsistent architecture from a consistently canonical HTTPS architecture.
Hostname Consistency
A website can use either a naked domain or a www hostname as its preferred architecture.
For example:
and:
can both be technically valid website configurations.
The important issue is whether the site consistently chooses one destination and redirects the alternative version appropriately.
The PKCapra checker therefore compares the four variations rather than assuming that either www or naked-domain architecture is universally correct.
HTTP/HTTPS Redirects and SEO
Redirect architecture is closely related to technical SEO because search engines need to understand how alternative URL versions relate to one another.
Inconsistent redirects can create unnecessary URL variations and additional crawl paths.
A clear redirect architecture can help establish the preferred protocol and hostname.
However, redirects are only one part of technical SEO.
Other signals include:
- Canonical URLs
- XML sitemaps
- Robots.txt
- Internal links
- Crawlability
- Indexability
- HTTP status codes
- URL structure
Use the Canonical URL Checker to investigate canonical signals separately.
Use the HTTP Status Checker to inspect individual HTTP response behavior.
HTTP/HTTPS Redirects and Canonical URLs
Redirects and canonical tags communicate different signals.
A redirect tells the browser or crawler to request another URL.
A canonical tag identifies the preferred URL representation of a page.
For example, a website may redirect:
http://example.com/page
to:
and the destination page may also specify:
as its canonical URL.
Keeping these signals aligned can reduce ambiguity.
Use the Canonical URL Checker when a redirect architecture appears correct but canonical signals require additional investigation.
HTTP/HTTPS Redirects and Crawlability
A redirect that technically works may still create unnecessary crawling complexity if it requires multiple hops.
Redirect chains can increase the number of requests needed before a crawler reaches the final destination.
Use the Crawlability Checker to investigate broader URL accessibility and crawling conditions.
HTTP/HTTPS Redirects and Indexability
Redirect behavior also affects how individual URLs are treated for indexing.
A URL that permanently redirects does not normally function like an independently indexable content URL.
A URL returning a successful 200 response may have different indexing implications.
Use the Indexability Checker when you need to investigate indexing signals beyond redirect behavior.
HTTP/HTTPS Redirects and XML Sitemaps
XML sitemaps should generally contain the preferred URLs that you want search engines to discover.
If sitemap URLs point to HTTP versions that immediately redirect to HTTPS, the sitemap architecture may require review.
Use the XML Sitemap Analyzer to inspect sitemap URLs and identify potential redirect relationships.
HTTP/HTTPS Redirects and Robots.txt
Robots.txt can also contain absolute URLs, particularly sitemap declarations.
After changing a website’s preferred hostname or HTTPS architecture, robots.txt should be reviewed to ensure that its references remain consistent.
Use the Robots.txt Analyzer to inspect robots.txt configuration.
How to Use the HTTP/HTTPS Redirect Checker
Step 1: Enter the Domain
Enter a naked or partial domain.
Examples include:
example.com
www.example.com
http://www.example.com
The checker normalizes the supplied domain before constructing the four core variations.
Step 2: Click Check Redirects
Click the Check Redirects button.
The scanner performs four independent server-side requests.
It does not require a third-party redirect API.
Step 3: Review the Four Variations
Review each of the four tested URL variations.
For each variation, inspect:
- Initial URL
- HTTP status
- Redirect count
- Final destination
- Secure protocol status
- Diagnostic classification
Step 4: Review the Canonical Choice
Review the Canonical Choice identified by the tool.
This represents the secure destination toward which the tested variations converge.
Step 5: Review Destination Agreement
Check whether all four variations resolve to the same final destination.
Uniform destination agreement is an important part of a clean protocol and hostname architecture.
Step 6: Review Redirect Chains
If a variation requires multiple hops, inspect the redirect sequence.
Determine whether the additional hops are intentional or whether the server configuration can send the request directly to the final destination.
Common Redirect Configuration Problems
HTTP Does Not Redirect
If the HTTP version returns a normal page instead of redirecting to HTTPS, inspect the web server or hosting configuration.
Possible configuration layers include:
- Apache
- Nginx
- CDN
- Reverse proxy
- Hosting control panel
- WordPress
- Redirect plugins
WWW and Naked Domain Disagree
If example.com and www.example.com resolve to different final destinations, review the preferred hostname configuration.
Decide which hostname should represent the primary website and configure the alternative version accordingly.
HTTPS and HTTP Use Different Destinations
If HTTP and HTTPS variations resolve to unrelated destinations, review:
- Server rules
- CDN configuration
- DNS configuration
- Reverse proxy settings
- WordPress URL configuration
- Redirect plugins
Redirect Chain Is Too Long
If a request passes through several redirects, review whether the initial URL can redirect directly to the final destination.
For example, instead of:
http://example.com
→ 301
→ http://www.example.com
→ 301
→ https://www.example.com
a direct redirect may be:
http://example.com
→ 301
→ https://www.example.com
Redirect Ends on HTTP
A redirect that ultimately reaches HTTP should be investigated because the final destination is not secure.
Review server, proxy, CDN, and WordPress redirect rules.
Redirect Returns 404
A 404 final response indicates that the requested redirect path ultimately reached a resource that the server considers not found.
Review the destination URL and redirect configuration.
Redirect Returns 500
A 500 final response indicates a server-side failure.
The problem may originate from:
- Application code
- Server configuration
- PHP
- Plugins
- Reverse proxy
- CDN
- Infrastructure
The redirect itself may be functioning while the destination application is failing.
Redirect Request Times Out
A timeout can indicate network, DNS, server, firewall, CDN, or infrastructure problems.
A timeout should not be interpreted as a successful redirect.
WordPress Redirect Architecture
WordPress websites can generate redirects through several layers.
Possible sources include:
- WordPress core
- SEO plugins
- Redirect plugins
- Theme code
.htaccess- Nginx configuration
- Hosting control panel
- CDN
- Reverse proxy
When several systems manage redirects simultaneously, conflicting rules can create unexpected chains or loops.
If a redirect problem appears after changing WordPress settings, review both WordPress URL configuration and server-level redirect rules.
CDN and Reverse Proxy Redirects
Modern websites frequently use CDNs and reverse proxies.
These systems can perform HTTPS redirects before the request reaches WordPress.
As a result, the final behavior observed by a diagnostic tool may be generated by:
- CDN edge rules
- Load balancers
- Reverse proxies
- Origin web servers
- WordPress
- Application middleware
When troubleshooting redirects, identify which infrastructure layer is actually generating the response.
Redirect Audit Checklist
Use this checklist when reviewing a website’s HTTP/HTTPS redirect architecture:
- HTTP naked domain responds correctly
- HTTP WWW domain responds correctly
- HTTPS naked domain responds correctly
- HTTPS WWW domain responds correctly
- HTTP variations redirect to HTTPS where intended
- Final destinations use HTTPS
- Final destinations use the intended hostname
- All four variations agree on one canonical destination
- Permanent redirects are used where permanent enforcement is intended
- Temporary redirects are reviewed
- Redirect chains are minimized
- Redirect loops are absent
- No final HTTP destination exists
- No unexpected external destination exists
- No critical 4xx response occurs
- No critical 5xx response occurs
- No request timeout occurs
- Canonical URLs match the intended destination
- XML sitemap URLs use preferred URLs
- Robots.txt references remain consistent
When Should You Run a Redirect Check?
The HTTP/HTTPS Redirect Checker is particularly useful when:
- Launching a new website
- Migrating from HTTP to HTTPS
- Changing the preferred
wwwor naked hostname - Migrating hosting providers
- Changing DNS
- Moving behind a CDN
- Configuring Cloudflare or another proxy
- Changing Apache rules
- Changing Nginx configuration
- Installing a redirect plugin
- Migrating WordPress
- Changing domain names
- Troubleshooting redirect chains
- Troubleshooting redirect loops
- Investigating SEO canonicalization problems
- Performing a technical SEO audit
Running the checker after major infrastructure changes can help verify that all four core URL variations still resolve consistently.
Traffic-Light Interpretation
The checker uses three primary diagnostic states.
Green — Optimal Redirect Configuration
A Green result indicates that the tested variation reaches the intended secure canonical architecture with the expected redirect behavior.
Typical conditions include:
- HTTPS final destination
- Direct permanent 301 where appropriate
- No unnecessary redirect chain
- Destination agreement
- Successful final response
Yellow — Needs Review
A Yellow result indicates that the URL resolves but the redirect architecture is not fully optimal.
Typical conditions include:
- 302 redirect
- 307 redirect
- Multiple redirect hops
- Destination disagreement
- Other non-uniform redirect behavior
Red — Critical
A Red result indicates a critical failure.
Typical conditions include:
- Timeout
- cURL failure
- 404 final response
- 500 final response
- Final HTTP destination
- Redirect crash
- Other fatal diagnostic conditions
Redirect Checker Limitations
The PKCapra HTTP/HTTPS Redirect Checker performs server-side requests and evaluates the responses returned by the target infrastructure.
Some behavior can depend on the requesting environment.
User-Agent Differences
Web servers can return different responses depending on the User-Agent.
The checker uses a modern desktop Chrome User-Agent to provide a browser-like diagnostic request.
Geographic Routing
CDNs and load-balancing systems can return different destinations based on geographic location.
A server-side diagnostic from one environment may therefore differ from a visitor’s experience in another region.
Cookie-Based Routing
Some websites change redirect behavior based on cookies or session state.
The checker uses an in-memory cookie jar during each diagnostic request but does not reproduce every possible visitor session.
JavaScript Redirects
Redirects performed exclusively through client-side JavaScript may not behave the same way as HTTP-level redirects.
The checker focuses primarily on server-side HTTP redirect behavior.
Authentication and Protected Resources
Authentication-protected URLs may require credentials or session information that the diagnostic tool does not possess.
The resulting response should therefore be interpreted in the context of the target’s access requirements.
Frequently Asked Questions
What is an HTTP/HTTPS Redirect Checker?
An HTTP/HTTPS Redirect Checker analyzes how the HTTP and HTTPS versions of a domain resolve and whether the different hostname and protocol combinations converge on one preferred secure destination.
How many URL variations does the PKCapra Redirect Checker test?
The checker tests four core variations:
- HTTP naked
- HTTP WWW
- HTTPS naked
- HTTPS WWW
Can I enter just a domain name?
Yes. You can enter a naked domain such as example.com, and the checker reconstructs the required protocol and hostname variations.
Does the tool require an API?
No. The PKCapra HTTP/HTTPS Redirect Checker performs its diagnostics server-side without a third-party redirect API.
What is a 301 redirect?
A 301 is a permanent redirect response.
What is a 302 redirect?
A 302 is a temporary redirect response.
What is a 307 redirect?
A 307 is a temporary redirect that preserves request method semantics.
What is a 308 redirect?
A 308 is a permanent redirect that preserves request method semantics.
Why should all four URL variations be checked?
Testing all four variations can reveal inconsistencies that a single URL test may miss.
For example, the naked HTTP domain may redirect correctly while the www HTTPS version behaves differently.
Should HTTP always redirect to HTTPS?
If HTTPS is the intended secure version of the website, HTTP requests will commonly be redirected to HTTPS. The exact implementation depends on the site’s architecture.
Should I always use 301?
A 301 is commonly used for permanent URL changes, but redirect status should reflect the actual purpose of the redirect. Temporary routing should not be incorrectly represented as permanent.
Why is my redirect chain marked Yellow?
A Yellow result can indicate multiple redirect hops. The destination may still be correct, but the chain can potentially be simplified.
Why is my redirect marked Red?
Red indicates a critical condition such as a timeout, server failure, final HTTP destination, or other diagnostic failure.
Why do www and non-www URLs produce different results?
The website may not have a consistent hostname canonicalization strategy, or different infrastructure layers may be handling the two hostnames differently.
Can redirect consistency affect SEO?
Redirect architecture can contribute to consistent URL signals and efficient crawling. However, redirects are only one part of technical SEO.
Can the checker detect redirect loops?
The diagnostic engine tracks redirect behavior and can identify critical redirect failures where a final usable destination cannot be reached.
Does the tool check SSL certificates?
The HTTP/HTTPS Redirect Checker focuses on protocol and redirect architecture. For dedicated certificate, HSTS, and mixed-content analysis, use the HTTPS Checker.
What should the canonical destination be?
The preferred canonical destination depends on the website’s architecture. It may use the naked domain or the www hostname. The important requirement is consistency.
Final HTTP/HTTPS Redirect Checklist
A clean redirect architecture should generally provide:
- One clearly preferred HTTPS destination
- Consistent hostname selection
- HTTP redirected to HTTPS where appropriate
- Permanent redirects for permanent URL changes
- Minimal redirect hops
- No redirect loops
- No final insecure HTTP destinations
- No unexpected external destinations
- Successful final responses
- Consistent canonical URLs
- Consistent sitemap URLs
- Consistent robots.txt references
- Consistent internal linking
The goal is not to force every website to use the same hostname structure. The goal is to make the chosen URL architecture clear, consistent, secure, and technically efficient.
Check All Four HTTP and HTTPS Variations
Use the PKCapra HTTP/HTTPS Redirect Checker to test the four primary protocol and hostname variations of your domain and identify whether they converge on one secure canonical destination.
For broader technical SEO analysis, combine the results with the Full SEO Site Audit, Technical SEO Checker, HTTPS Checker, Canonical URL Checker, Redirect Checker, HTTP Status Checker, Crawlability Checker, and Indexability Checker.
Run the checker after domain migrations, HTTPS migrations, hosting changes, CDN changes, redirect-rule changes, or hostname configuration changes to verify that your complete HTTP/HTTPS architecture continues to resolve consistently.