
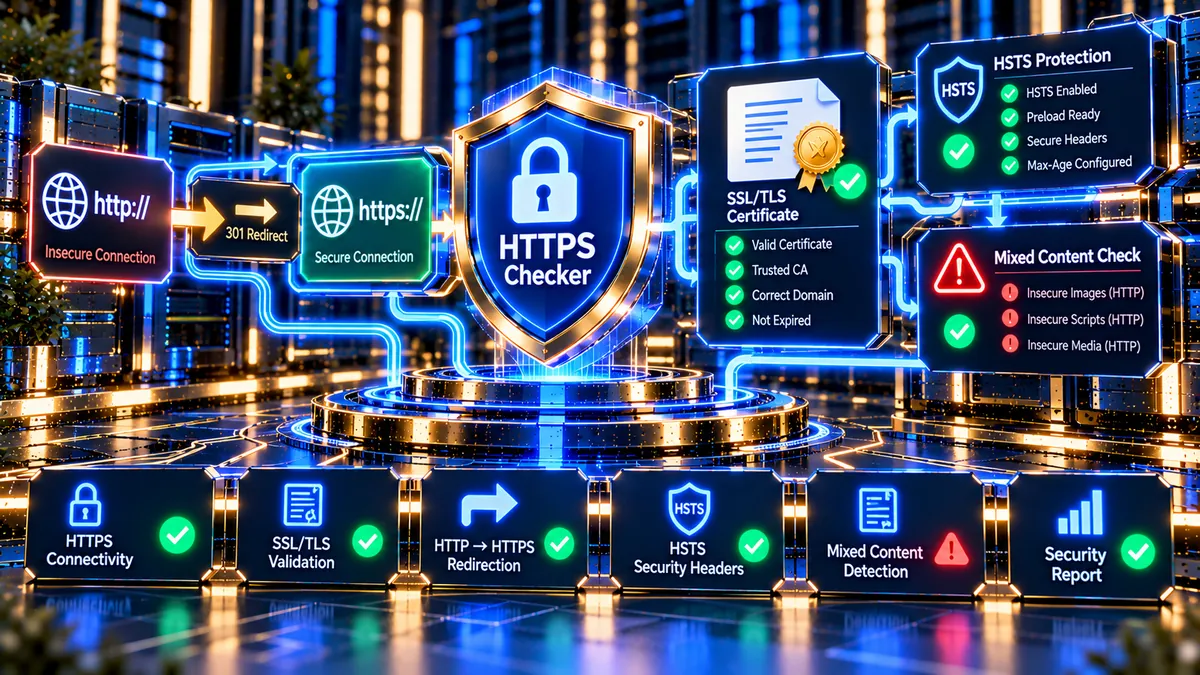
The PKCapra HTTPS Checker is a free technical SEO and website security diagnostic tool that analyzes how a website implements HTTPS, HTTP-to-HTTPS redirects, HSTS security headers, mixed-content resources, and SSL/TLS certificate validity.
Enter a website URL below to inspect its HTTPS configuration and identify important transport-security issues from a single technical dashboard.
HTTPS Checker
Audit HTTPS transport, HSTS enforcement, mixed-content inheritance, HTTP-to-HTTPS redirects, and TLS certificate lifespan from the server side.
HTTPS implementation analysis
—
Strict-Transport-Security
Validity window
Insecure resource inheritance
| Type | HTTP Resource | Source Attribute |
|---|
HTTP counterpart redirect
Live response details
HTTPS implementation checkpoints
The HTTPS Checker is designed for website owners, WordPress developers, technical SEO professionals, agencies, system administrators, and anyone troubleshooting HTTPS implementation problems.
It performs server-side diagnostics without requiring a third-party HTTPS analysis API.
The checker evaluates:
- HTTPS response status
- HTTP-to-HTTPS enforcement
- Redirect status codes
- Redirect destination
- HTTPS protocol validation
- Domain and hostname alignment
- HSTS header presence
- HSTS max-age
- HSTS preload configuration
- Mixed-content resources
- SSL/TLS certificate validity
- Certificate expiration date
- Certificate remaining lifespan
- HTTPS response information
For a wider technical investigation, use the Full SEO Site Audit to analyze HTTPS together with other technical SEO signals.
What Is an HTTPS Checker?
An HTTPS Checker is a diagnostic tool that examines whether a website is correctly configured to use HTTPS and whether its secure transport implementation is working consistently.
HTTPS configuration involves more than simply installing an SSL/TLS certificate.
A complete HTTPS implementation should normally include:
- A working HTTPS endpoint
- A valid TLS certificate
- Correct HTTP-to-HTTPS redirection
- An appropriate permanent redirect where permanent HTTPS enforcement is intended
- A valid HSTS configuration where appropriate
- No unnecessary insecure HTTP resources
- Consistent HTTPS URL architecture
- Proper certificate expiration monitoring
The PKCapra HTTPS Checker brings these diagnostic areas together in one server-side analysis.
Why HTTPS Is Important
HTTPS encrypts communication between a visitor’s browser and a website server using TLS.
This helps protect information transmitted between the visitor and the website and provides a secure transport layer for web requests.
HTTPS is also important for maintaining a consistent website URL architecture.
A website can technically have several versions of the same URL:
http://example.com/https://example.com/http://www.example.com/https://www.example.com/
A properly configured website should establish its intended secure version and consistently handle alternative protocol or hostname variations.
For example, an HTTP request may redirect to an HTTPS destination such as http://example.com/page → 301 → https://www.example.com/page.
The exact hostname depends on the website’s architecture, but the important principle is that the website should have a clear and consistent secure destination.
HTTPS should also remain consistent across canonical URLs, XML sitemaps, redirects, internal links, and other technical SEO signals.
What Does the PKCapra HTTPS Checker Analyze?
The PKCapra HTTPS Checker performs several independent diagnostic checks.
HTTPS Response
The first checkpoint examines the secure HTTPS endpoint and records the response returned by the server.
The diagnostic can identify:
- HTTP status code
- HTTPS endpoint
- Response status
- Content type
- Server information when available
- Secure endpoint response details
A successful HTTPS response confirms that the inspected endpoint is responding, but it does not automatically prove that the entire HTTPS implementation is correctly configured.
A website can return a successful HTTPS response while still having:
- Missing HSTS
- Mixed content
- Incorrect HTTP redirects
- An expiring certificate
- Inconsistent hostname configuration
The checker therefore continues with additional HTTPS diagnostics.
HTTP-to-HTTPS Redirect Checker
One of the most important HTTPS checks is determining what happens when someone requests the HTTP version of a website.
For example:
http://example.com/
may redirect to:
The PKCapra HTTPS Checker analyzes the HTTP response and examines the redirect destination.
It recognizes common redirect statuses including:
- 301 Permanent Redirect
- 302 Temporary Redirect
- 307 Temporary Redirect
- 308 Permanent Redirect
Why a 301 Redirect Matters
A 301 response communicates that the requested URL has been permanently moved to another location.
When HTTPS is intended to be the permanent version of a website, a permanent redirect can establish a clear relationship between the HTTP and HTTPS versions.
Temporary redirect responses such as 302 or 307 communicate different redirect behavior and should be reviewed when permanent HTTPS enforcement is intended.
The correct redirect status ultimately depends on the website’s architecture and migration requirements.
Redirect Destination Validation
The PKCapra HTTPS Checker does not rely on a simple full-string comparison between the original HTTP URL and the redirect URL.
Real-world websites commonly use legitimate hostname variations.
For example:
http://example.com/
may redirect to:
This can be a valid hostname canonicalization pattern.
The checker therefore analyzes the individual URL components and evaluates the redirect destination based on its scheme and hostname.
The validation handles common variations including:
example.comwww.example.com- Trailing slashes
- URL paths
- Query strings
- URL fragments
- Explicit port information
The destination must use the HTTPS scheme.
The destination must also belong to the intended domain architecture.
This prevents a completely unrelated external domain from being treated as a successful HTTPS enforcement destination.
HSTS Checker
HSTS stands for HTTP Strict Transport Security.
It is implemented through the Strict-Transport-Security HTTP response header.
A basic HSTS configuration may look like:
Strict-Transport-Security: max-age=31536000
A more extensive configuration may include:
Strict-Transport-Security: max-age=31536000; includeSubDomains; preload
The PKCapra HTTPS Checker detects the HSTS header and analyzes its configuration.
The report can identify:
- HSTS header presence
- HSTS max-age
- Preload directive
- HSTS classification
Understanding HSTS max-age
The max-age directive specifies how long a compatible browser should remember the HSTS policy.
The value is measured in seconds.
For example:
max-age=31536000
represents approximately one year.
A longer policy duration can provide more persistent HTTPS enforcement after a browser receives the policy.
However, HSTS should be deployed carefully.
Before implementing a long-duration HSTS policy, website owners should verify that all required pages, services, subdomains, resources, and applications work correctly over HTTPS.
HSTS Preload
The preload directive is associated with browser HSTS preload mechanisms.
The PKCapra HTTPS Checker identifies whether the response contains the preload token.
However, the presence of preload in the HSTS header does not by itself prove that a domain has been accepted into a browser preload list.
These are separate concepts.
The checker therefore reports the response-header configuration independently.
Mixed Content Scanner
Mixed content occurs when an HTTPS document attempts to load resources through insecure HTTP URLs.
For example, an image may contain an insecure reference such as http://example.com/image.jpg.
A script may contain an insecure reference such as http://example.com/script.js.
The PKCapra HTTPS Checker scans the returned HTML payload for hardcoded HTTP resource references.
The scanner can inspect resources associated with:
- Images
- JavaScript
- Stylesheets
- Iframes
- Video
- Audio
- Object elements
- Embedded resources
- Poster attributes
srcset- CSS
url()references - Other server-visible resource attributes
A result showing zero resources means that the server-side HTML scan did not detect the supported hardcoded HTTP references in the returned page.
Why Mixed Content Matters
An HTTPS document should ideally load its resources through HTTPS as well.
Insecure resources can create security problems and may be blocked or restricted by modern browsers.
Mixed-content problems can originate from many parts of a website, including:
- WordPress themes
- WordPress plugins
- Database content
- Hardcoded image URLs
- CSS files
- JavaScript
- Third-party embeds
- External widgets
- Old URLs remaining after an HTTPS migration
When mixed content is detected, identify the actual source of the insecure reference before changing the URL.
Server-Side Mixed Content Limitations
The PKCapra HTTPS Checker performs a server-side analysis of the returned HTML.
It does not execute every JavaScript instruction in a real browser.
For example, JavaScript can dynamically create a resource after the initial HTML response.
An insecure resource generated only after JavaScript execution may therefore not appear in the server-side HTML scan.
For advanced browser-side investigation, browser developer tools can be used alongside the PKCapra result.
SSL/TLS Certificate Checker
HTTPS depends on a valid TLS certificate.
The PKCapra HTTPS Checker establishes a TLS connection and examines the peer certificate presented by the server.
The certificate analysis can provide:
- Certificate validity start
- Certificate expiration date
- Certificate remaining lifespan
- Certificate Common Name when available
The remaining certificate lifespan is calculated from the certificate’s actual expiration timestamp and the current server execution time.
This provides a practical indication of whether a certificate is healthy, approaching expiration, or already expired.
Certificate Expiration
A TLS certificate should be renewed before it expires.
An expired certificate can cause browsers and other clients to display certificate warnings or prevent normal secure connections.
The HTTPS Checker calculates the remaining validity period using the certificate expiration timestamp.
The dashboard uses diagnostic ranges such as:
- More than 30 days remaining: healthy certificate lifespan
- 8 to 30 days remaining: attention recommended
- Under 7 days remaining: critical expiration window
- Expired certificate: critical condition
These classifications are intended to make certificate-management issues easier to identify during a technical audit.
Automated certificate renewal should still be configured through the hosting environment, certificate provider, or infrastructure-management system where possible.
HTTPS Traffic-Light Status
The HTTPS Checker uses traffic-light classifications to make technical findings easier to understand.
Green Status
Green indicates that the corresponding diagnostic checkpoint satisfies the tool’s configured validation criteria.
Examples include:
- Successful HTTPS response
- Correct permanent HTTP-to-HTTPS enforcement
- HTTPS redirect destination
- Redirect destination aligned with the intended domain architecture
- No detected mixed-content resources
- Healthy TLS certificate lifespan
- Strong HSTS configuration
Yellow or Orange Status
Yellow or orange identifies a condition that should be reviewed.
Examples include:
- Temporary HTTP redirect
- HSTS present without the expected preload configuration
- Certificate approaching expiration
- Partial HTTPS configuration
A yellow result does not necessarily mean that the website is insecure. It indicates that the specific configuration should be reviewed.
Red Status
Red indicates a more significant diagnostic problem.
Examples include:
- HTTP endpoint not correctly secured
- Missing HSTS header
- Incorrect HTTPS redirect destination
- Certificate approaching critical expiration
- Expired certificate
- Other critical HTTPS configuration conditions
The traffic-light result is a diagnostic classification. Always review the detailed response information before changing a production configuration.
How to Use the PKCapra HTTPS Checker
Step 1: Enter Your URL
Enter the website or endpoint you want to analyze.
For example:
You can also enter an HTTP URL when you specifically want to investigate HTTP-to-HTTPS enforcement.
Step 2: Click Check HTTPS
Click the Check HTTPS button.
The checker performs the diagnostic from the server side.
The engine examines the HTTPS response, HTTP redirect behavior, HSTS configuration, returned HTML, mixed-content references, and TLS certificate.
Step 3: Review the Diagnostic Summary
Start with the Diagnostic Summary.
This section provides an overview of the HTTPS implementation and highlights conditions that require attention.
Step 4: Review HSTS
Review the HSTS Configuration section.
Pay attention to:
- Header status
- Max-age
- Preload configuration
- Classification
If HSTS is missing, evaluate whether the site’s HTTPS architecture is sufficiently stable before implementing an HSTS policy.
Step 5: Review Mixed Content
Review the Mixed Content Scanner.
If zero insecure resources are reported, the inspected HTML did not expose supported hardcoded HTTP resources.
If resources are detected, review each resource and its source attribute to determine where the insecure reference originates.
Step 6: Review HTTP Enforcement
Review the HTTP Enforcement section.
Check:
- HTTP status
- Redirect destination
- HTTPS scheme
- Destination hostname
- Permanent or temporary redirect classification
A properly configured permanent HTTPS migration will generally use a permanent redirect toward the intended HTTPS domain.
Step 7: Review TLS Certificate
Review the TLS Certificate section.
Check:
- Valid-from date
- Valid-to date
- Days remaining
- Common Name
If the certificate is approaching expiration, arrange renewal before the certificate becomes invalid.
Common HTTPS Problems
HTTP and HTTPS Both Serve the Website
If both HTTP and HTTPS versions independently serve content, the website may lack consistent protocol enforcement.
Review the web server, CDN, reverse proxy, or WordPress redirect configuration.
HTTP Does Not Redirect to HTTPS
An HTTP endpoint that does not redirect to HTTPS should be investigated.
Possible configuration locations include:
- Apache
- Nginx
- CDN
- Reverse proxy
- Hosting control panel
- WordPress
- Redirect plugins
HTTP Uses a Temporary Redirect
A 302 or 307 response may indicate temporary redirect behavior.
If HTTPS is intended to be the permanent protocol, review whether permanent redirect behavior is more appropriate for the site’s architecture.
Redirect Goes to an Unexpected Domain
An HTTPS redirect should be investigated carefully if the destination is an unrelated external domain.
Review:
- Server redirect rules
- CDN configuration
- Reverse proxy rules
- WordPress redirect plugins
- Domain configuration
- Application-level redirects
HSTS Is Missing
A missing HSTS header does not mean that the TLS certificate is invalid.
HTTPS and HSTS are separate security layers.
If HSTS is required for the site’s security architecture, configure the response header at the appropriate server, CDN, or application layer.
Mixed Content Is Detected
If insecure resources are detected, identify where the HTTP URL originates.
Possible sources include:
- Theme files
- Plugin settings
- Database content
- CSS
- JavaScript
- Image URLs
- Third-party embeds
Replace insecure references with HTTPS versions where the resource supports HTTPS.
Certificate Is Near Expiration
If the certificate has a short remaining lifespan, review the renewal process promptly.
Do not wait until the certificate has expired before investigating certificate management.
HTTPS and WordPress
WordPress websites can develop HTTPS inconsistencies after migrations, domain changes, hosting changes, CDN deployments, or plugin configuration changes.
Important areas to review include:
- WordPress Address
- Site Address
- Theme URLs
- Plugin URLs
- Media URLs
- Database content
- Canonical URLs
- XML sitemap URLs
- Redirect rules
- CDN settings
A homepage may work correctly over HTTPS while individual posts, images, scripts, or other resources still use HTTP.
This is why a complete HTTPS review should examine more than the homepage.
HTTPS and Canonical URLs
HTTPS redirects and canonical URLs serve different purposes.
A redirect tells a browser or crawler where a requested URL should go.
A canonical URL identifies the preferred URL representation of a page.
For example:
http://example.com/page
may redirect to:
while the canonical URL may also identify:
Keeping these signals consistent can help reduce URL ambiguity.
Use the Canonical URL Checker when you need to investigate canonical configuration separately.
HTTPS and Crawlability
A valid HTTPS certificate does not automatically mean that every page on a website can be crawled.
Crawlability can also be affected by:
- Robots.txt
- Server errors
- Redirect chains
- Blocked resources
- Authentication
- Network restrictions
- Internal linking
Use the Crawlability Checker to investigate whether important URLs can be reached by crawlers.
HTTPS and Indexability
HTTPS is also separate from indexability.
A page can work perfectly over HTTPS while still being excluded from search indexing through other signals.
Indexability can be affected by:
noindex- Canonical directives
- Robots.txt
- HTTP status
- Redirects
- Duplicate URL structures
Use the Indexability Checker when you need to inspect indexability signals.
HTTPS and XML Sitemaps
XML sitemaps should normally contain the intended HTTPS URLs of the website.
After an HTTP-to-HTTPS migration, old HTTP URLs can sometimes remain inside sitemap files.
This can create unnecessary redirects and inconsistent URL signals.
Use the XML Sitemap Analyzer to inspect sitemap URLs and structure.
HTTPS and Robots.txt
Robots.txt should also be reviewed after an HTTPS migration.
Sitemap declarations and other absolute URLs should use the intended website architecture.
Use the Robots.txt Analyzer to inspect robots.txt configuration.
HTTPS and Redirects
HTTPS implementation is closely connected with redirect architecture.
Redirect problems can include:
- Missing redirects
- Temporary redirects
- Redirect chains
- Redirect loops
- Incorrect domains
- HTTP destinations
- HTTPS destinations on unintended hostnames
Use the Redirect Checker when you need a dedicated redirect analysis.
For individual HTTP response analysis, the HTTP Status Checker can provide additional information.
HTTPS and Broader Technical SEO
HTTPS is only one part of technical SEO.
A website can have a valid TLS certificate while still experiencing problems with:
- Crawlability
- Indexability
- Canonical URLs
- Redirects
- XML sitemaps
- Robots.txt
- Internal links
- URL structure
- Page performance
- Duplicate URLs
For a broader technical analysis, use the Technical SEO Checker together with the HTTPS Checker.
For a complete website-level investigation, use the Full SEO Site Audit.
HTTPS Audit Checklist
Use this checklist when reviewing a website’s HTTPS implementation:
- HTTPS endpoint responds successfully
- HTTP endpoint redirects toward HTTPS
- Redirect uses the intended status
- Redirect destination uses HTTPS
- Redirect destination belongs to the intended domain architecture
- HSTS header has been reviewed
- HSTS max-age has been reviewed
- HSTS preload configuration has been reviewed
- No hardcoded HTTP image resources were detected
- No hardcoded HTTP script resources were detected
- No hardcoded HTTP stylesheet resources were detected
- No insecure iframe resources were detected
- TLS certificate is valid
- Certificate expiration is monitored
- HTTPS URLs are consistent with canonical URLs
- XML sitemap URLs use the intended HTTPS architecture
- Robots.txt references are consistent
- Important URLs remain crawlable
- Important URLs remain indexable
When Should You Run an HTTPS Check?
The HTTPS Checker is useful during:
- New website launches
- HTTP-to-HTTPS migrations
- WordPress migrations
- Hosting migrations
- Domain migrations
- CDN changes
- DNS changes
- SSL certificate installation
- SSL certificate renewal
- Web server configuration changes
- Reverse proxy changes
- Redirect troubleshooting
- Mixed-content troubleshooting
- HSTS implementation
- Technical SEO audits
Running the checker after major infrastructure changes can help verify that the intended HTTPS configuration remains active.
HTTPS Checker Limitations
The PKCapra HTTPS Checker is a server-side diagnostic tool.
Some browser-only behavior is therefore outside its scope.
Dynamically Generated Resources
Resources created by JavaScript after the initial HTML response may not appear in the mixed-content scan.
Browser-Specific Security Behavior
The checker does not reproduce every security decision made by every browser.
HSTS Preload List Membership
Detecting the preload directive in the HSTS header does not prove that a domain has been accepted into a browser preload list.
Certificate Trust Environment
The checker focuses on certificate information exposed during the TLS connection. Complete PKI validation can require additional certificate-chain and client-environment testing.
Infrastructure Configuration
The checker reports what the inspected endpoint exposes. It does not automatically identify the exact Apache, Nginx, CDN, hosting, or WordPress configuration responsible for every response.
These limitations should be considered when interpreting the diagnostic results.
Frequently Asked Questions
What is an HTTPS Checker?
An HTTPS Checker analyzes a website’s HTTPS configuration, including SSL/TLS certificate validity, HTTP-to-HTTPS redirects, HSTS headers, and mixed-content resources.
Is the PKCapra HTTPS Checker free?
Yes. The PKCapra HTTPS Checker is provided as a free technical diagnostic tool.
Does the HTTPS Checker require an API?
No. The tool is designed for server-side execution without requiring a third-party HTTPS analysis API.
What does a 301 HTTPS redirect mean?
A 301 is a permanent redirect response. When an HTTP URL redirects to its intended HTTPS destination with a 301, it indicates a permanent redirect relationship.
Is a 302 redirect the same as a 301?
No. A 302 indicates temporary redirect behavior, while a 301 indicates permanent redirect behavior.
Why can example.com redirect to www.example.com and still be valid?
www is a hostname variation. If the website intentionally uses www as its preferred hostname, redirecting the non-www version to the www HTTPS version can be a normal hostname canonicalization pattern.
What is HSTS?
HSTS stands for HTTP Strict Transport Security. It is a response-header mechanism that tells compatible browsers to use HTTPS for future connections to a domain.
What is HSTS max-age?
HSTS max-age specifies how long a browser should remember the HSTS policy, measured in seconds.
What is mixed content?
Mixed content occurs when an HTTPS page loads resources through insecure HTTP URLs.
Can the HTTPS Checker find every mixed-content problem?
No. The checker analyzes server-returned HTML. Resources generated dynamically by JavaScript after page load may require browser-side inspection.
Can the HTTPS Checker detect an expired SSL certificate?
Yes. The checker analyzes the TLS peer certificate and calculates the remaining certificate validity period.
Why does my certificate show a certain number of days remaining?
The tool calculates remaining certificate lifespan from the certificate’s expiration timestamp relative to the current server execution time.
Does HTTPS automatically mean my website is technically SEO-friendly?
No. HTTPS is one part of technical website architecture. Crawlability, indexability, canonical URLs, redirects, sitemaps, robots.txt, internal links, performance, and other signals also matter.
Should every website use HSTS?
HSTS can provide valuable HTTPS enforcement, but it should be deployed according to the website’s infrastructure and operational requirements. Before applying a long-duration policy, verify that the relevant website and services consistently support HTTPS.
Why is my HTTP redirect marked temporary?
The server is returning a temporary redirect such as 302 or 307. If the HTTPS destination is intended to be permanent, review the redirect configuration.
Why is my certificate approaching expiration?
TLS certificates have defined validity periods. When the expiration date approaches, the certificate should be renewed through the site’s certificate-management process.
Can HTTPS Checker identify the exact server setting causing a problem?
The checker reports the behavior exposed by the target server. It does not automatically determine whether Apache, Nginx, a CDN, reverse proxy, WordPress, or another infrastructure component generated a particular response.
Final HTTPS Configuration Checklist
A technically consistent HTTPS implementation should include:
- A working HTTPS endpoint
- A valid TLS certificate
- Correct HTTP-to-HTTPS enforcement
- An appropriate redirect status
- A verified HTTPS redirect destination
- Consistent hostname architecture
- Appropriate HSTS configuration
- No unnecessary insecure resource references
- Certificate expiration monitoring
- Consistent canonical HTTPS URLs
- HTTPS XML sitemap URLs
- Consistent robots.txt references
- Crawlable important pages
- Indexable pages where appropriate
HTTPS should be considered part of the website’s overall technical architecture rather than an isolated SSL certificate installation.
Check Your Website’s HTTPS Configuration
Use the PKCapra HTTPS Checker to inspect HTTPS response behavior, HTTP-to-HTTPS enforcement, HSTS configuration, mixed-content resources, and TLS certificate lifespan from one technical diagnostic dashboard.
For a broader technical SEO investigation, combine the HTTPS Checker with the Full SEO Site Audit, Technical SEO Checker, Canonical URL Checker, Crawlability Checker, Indexability Checker, XML Sitemap Analyzer, Robots.txt Analyzer, and Redirect Checker.
Run the HTTPS Checker after major website, hosting, DNS, CDN, certificate, or redirect changes to verify that your HTTPS implementation continues to behave as intended.